Industry:Banking and Finance Added By:Admin Posted On:Nov. 20, 2026
Key points
The Nacha fraud monitoring rules that took effect in 2026 require every ODFI and every non-consumer Originator, Third-Party Service Provider (TPSP) and Third-Party Sender (TPS) to run risk-based processes that identify ACH entries suspected of being unauthorized or authorized under False Pretenses. RDFIs must monitor incoming ACH credits the same way. Phase 1 started March 20, 2026, and Phase 2 started June 19, 2026 (in practice Monday, June 22), so every covered party should already have a working, documented program.
Four Nacha Operating Rules changes took effect in 2026. The fraud monitoring rules are the largest; the sections below cover each one.
| Effective date | Rule change | Who it applies to |
|---|---|---|
| March 20, 2026 | Fraud monitoring Phase 1 | All ODFIs; non-consumer Originators, TPSPs and TPSs with 6 million or more 2023 ACH originations; RDFIs with 10 million or more 2023 ACH receipts |
| March 20, 2026 | “PAYROLL” and “PURCHASE” Company Entry Descriptions become mandatory | Originators of payroll PPD credits and of WEB debits for online purchases of goods |
| June 19, 2026 (June 22 in practice) | Fraud monitoring Phase 2 | All other non-consumer Originators, TPSPs, TPSs and RDFIs |
| September 18, 2026 | Non-Same Day ACH credits must be available by 9:00 a.m. RDFI local time on the Settlement Date | RDFIs |
Before these amendments, Nacha’s fraud detection requirements for Originators reached only WEB debits and Micro-Entries. The 2026 rules extend monitoring to ACH activity generally, including the credit-push payments that business email compromise and impersonation scams depend on.
The rules set out two obligations:
Both obligations include a review requirement. Each party must review its processes and procedures at least annually and update them to address evolving risks. Reviewing more often is allowed. The review fits naturally alongside the Nacha audit requirements, since the annual Rules Compliance Audit is due by December 31.
Nacha defines False Pretenses as the inducement of a payment by a person misrepresenting (a) their identity, (b) their association with or authority to act for another person, or (c) the ownership of the account to be credited. That covers business email compromise, vendor impersonation and payroll impersonation, where the payment is technically authorized but the payer was deceived. It does not cover scams involving fake, non-existent or poor-quality goods or services.
The rollout was split by 2023 ACH volume. Consumer Originators are not covered by the monitoring requirement.
| Who | Requirement | Effective date |
|---|---|---|
| All ODFIs, regardless of volume | Risk-based fraud monitoring of ACH entries, reviewed at least annually | March 20, 2026 (Phase 1) |
| Non-consumer Originators, TPSPs and TPSs with 2023 ACH origination volume of 6 million or more | Risk-based fraud monitoring of ACH entries, reviewed at least annually | March 20, 2026 (Phase 1) |
| RDFIs with 2023 ACH receipt volume of 10 million or more | Risk-based monitoring of incoming ACH credits (Subsection 3.1.10), reviewed at least annually | March 20, 2026 (Phase 1) |
| All other non-consumer Originators, TPSPs and TPSs | Risk-based fraud monitoring of ACH entries, reviewed at least annually | June 19, 2026; practical date June 22, 2026 (Phase 2) |
| All other RDFIs | Risk-based monitoring of incoming ACH credits, reviewed at least annually | June 19, 2026; practical date June 22, 2026 (Phase 2) |
| Originators of PPD credits for wages, salaries and similar pay to consumer accounts | Company Entry Description “PAYROLL” | March 20, 2026 |
| Originators of WEB debits to consumer accounts for online purchases of goods | Company Entry Description “PURCHASE” | March 20, 2026 |
Both are correct. Nacha’s Phase 2 rule page lists the effective date as June 19, 2026, then explains that because June 19 is a federal holiday (Juneteenth), the practical effective date is the next banking day, Monday, June 22, 2026. Use June 19 as the rule date and June 22 as the first processing day the rule applied to.
The Rules do not prescribe specific processes, procedures or software. Nacha’s Phase 1 rule page says solutions may be built in-house or bought from vendors, and that each party’s approach should fit its role, volume and risk. For the controls businesses use to stop these payments before they are sent, see how to prevent ACH fraud.
Several points from Nacha’s guidance shape what “risk-based” allows:
RDFI credit monitoring must include a risk assessment that separates higher-risk from lower-risk activity. The rule does not require pre-posting monitoring of credits. Nacha’s examples of warning signs include an SEC Code that doesn’t match the account type, unusually large amounts, bursts of similar credits, and activity on new, dormant or suspected money-mule accounts.
When an RDFI flags a credit, it can return it with R17, or with R06 if the ODFI asks for it back. An RDFI that monitors before posting may also use the funds availability exemption for suspect credits. RDFIs may use third-party service providers to meet these obligations. The full list of codes and deadlines is in the guide to ACH return codes.
No. Nacha says the amendments include express disclaimers that they do not modify rights and obligations under UCC Article 4A, and do not create any duty other than each party’s commitment to Nacha to comply with the Rules. Nacha states this lets it manage compliance without upsetting the allocation of liability among participants.
In practical terms, an RDFI that misses a False Pretenses credit does not become liable for the loss because of these rules, and an Originator tricked into paying an impostor does not gain a new claim against its bank. What changes is your rules compliance exposure. Nacha can enforce the monitoring and annual review requirements like any other Rule.
A separate rule in the same package, effective March 20, 2026, made two descriptions mandatory. These are required, not optional:
The ODFI has no obligation to check that “PURCHASE” is present or accurate, and RDFIs are not required to act on either description, though they may use it in their own monitoring. Details are on Nacha’s Company Entry Descriptions rule page.
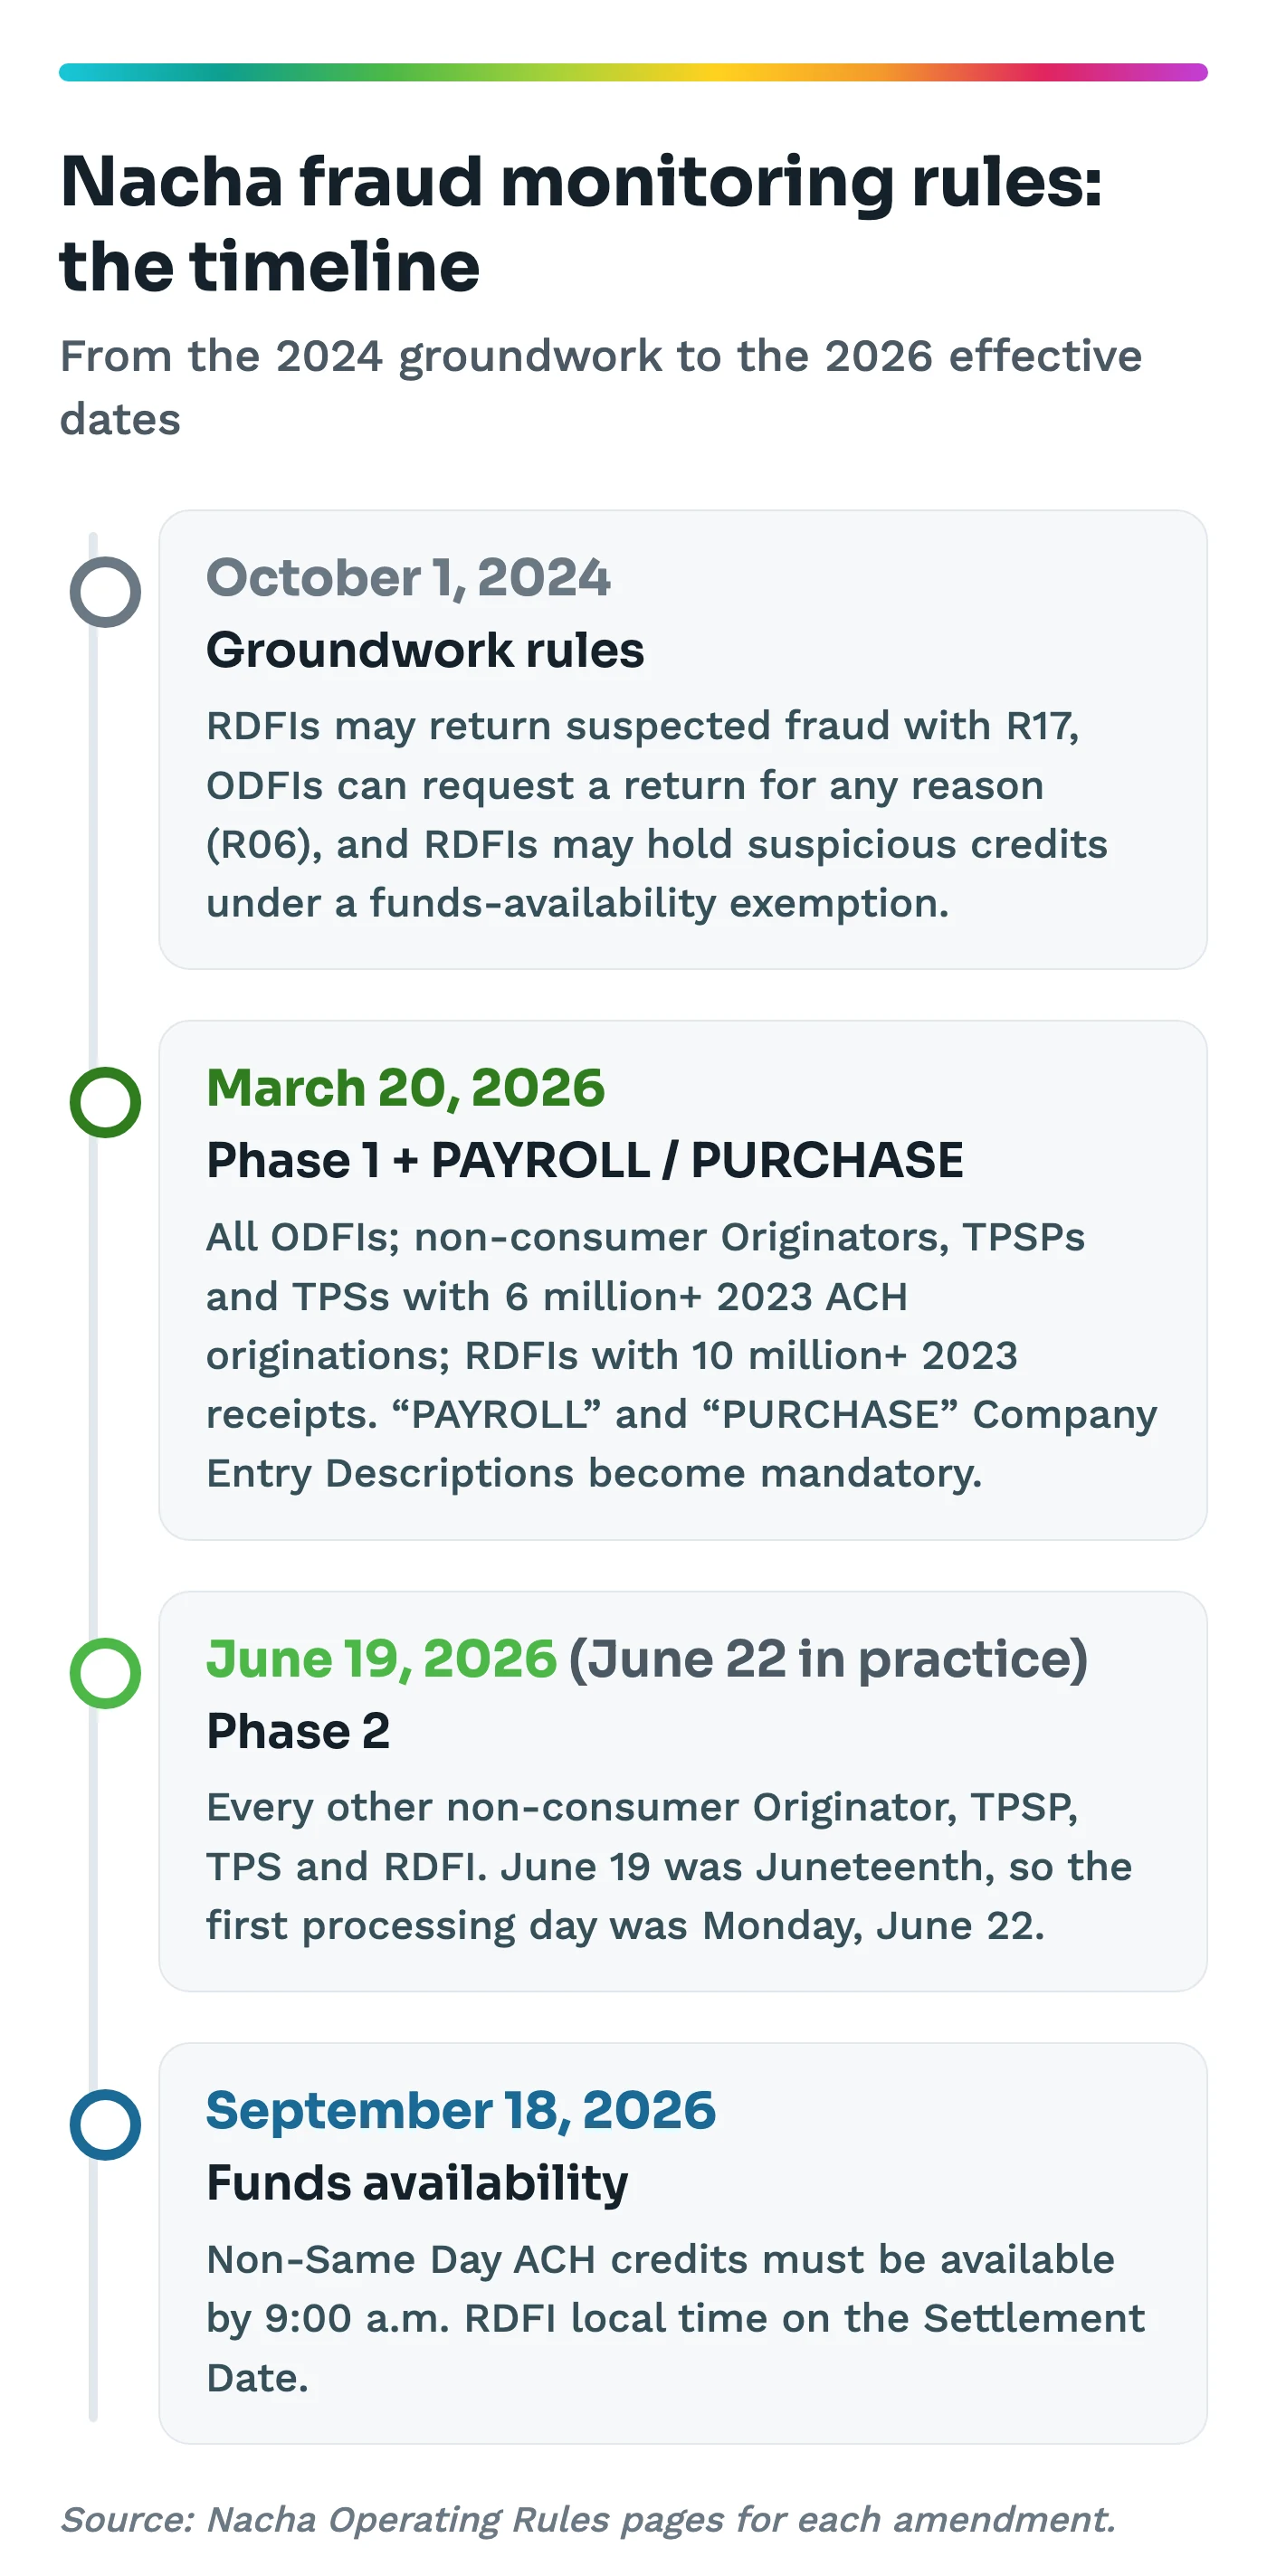
The 2026 monitoring rules close out a package Nacha approved in 2024. The first part took effect October 1, 2024, and gives RDFIs and ODFIs the tools to act on what their monitoring finds. Nacha’s October 1, 2024 rule page lists:
One more change affects RDFI posting. Under the non-Same Day credit funds availability rule effective September 18, 2026, funds for all non-Same Day credits must be available by 9:00 a.m. RDFI local time on the Settlement Date. If your credit monitoring runs before posting, check that alerts are worked within that window or that holds clearly fit the False Pretenses exemption.
Use this list to test whether your program would stand up in an ACH rules audit or an ODFI review:
The main 2026 changes require risk-based fraud monitoring by ODFIs, non-consumer Originators, TPSPs and TPSs, and risk-based monitoring of incoming ACH credits by RDFIs, phased in on March 20 and June 19, 2026. A related rule made the Company Entry Descriptions “PAYROLL” and “PURCHASE” mandatory from March 20, 2026. Nacha also has funds availability and IAT changes effective later in 2026 and 2027.
No. The Rules do not prescribe specific processes, procedures or products. Nacha says solutions may be built in-house or bought from vendors, as long as they are risk-based, fit your role and are reviewed at least annually.
Yes, if they originate ACH entries as non-consumer Originators. Phase 2, effective June 19, 2026, removed the volume threshold, so every non-consumer Originator is covered regardless of size. Consumer Originators are not covered.
It is a payment induced by someone misrepresenting their identity, their authority to act for another person, or the ownership of the account to be credited. Business email compromise, vendor impersonation and payroll redirect scams are typical examples. Scams over fake or poor-quality goods and services are not included.
No. Nacha says RDFIs do not have to screen every entry individually and are not required to monitor credits before posting. Monitoring must still be risk-based and include a risk assessment that separates higher-risk from lower-risk activity.
Phase 2 took effect June 19, 2026. Because June 19 is the Juneteenth federal holiday, Nacha says the practical effective date was the next banking day, Monday, June 22, 2026. Phase 2 covers every non-consumer Originator, TPSP, TPS and RDFI that Phase 1 did not, regardless of volume.
Get Nacha and ACH rule changes as they happen
The 247Compliance newsletter sends new rules, effective dates and upcoming payments webinars to your inbox.
SubscribeThis article is general information, not legal or tax advice. Check the official sources above or consult a qualified advisor for your situation.